Multimodal media integrity & forensic verification shield
Suryakavacham analyses media, not people. It correlates independent forensic signals into a transparent, uncertainty-aware integrity assessment — with encrypted evidence, sealed reports and a tamper-evident chain of custody.
Signed out, the console runs on a read-only sandbox corpus. Live case data requires an account.
- 0
- forensic modules
- 0-bit
- envelope encryption
- 0%
- actions hash-chained
- 0
- verdicts issued about people
Sandbox
The demonstration corpus loads only while this section is in view. Scroll back up to re-open it, or sign in to work with your own encrypted cases.
scroll depth 0%
See it before you sign up
The workflow, screen by screen
This is the real console workflow an analyst runs after signing in — ingest, analyse, review, seal. Nothing here is a verdict about a person; every screen is built to show evidence and uncertainty.
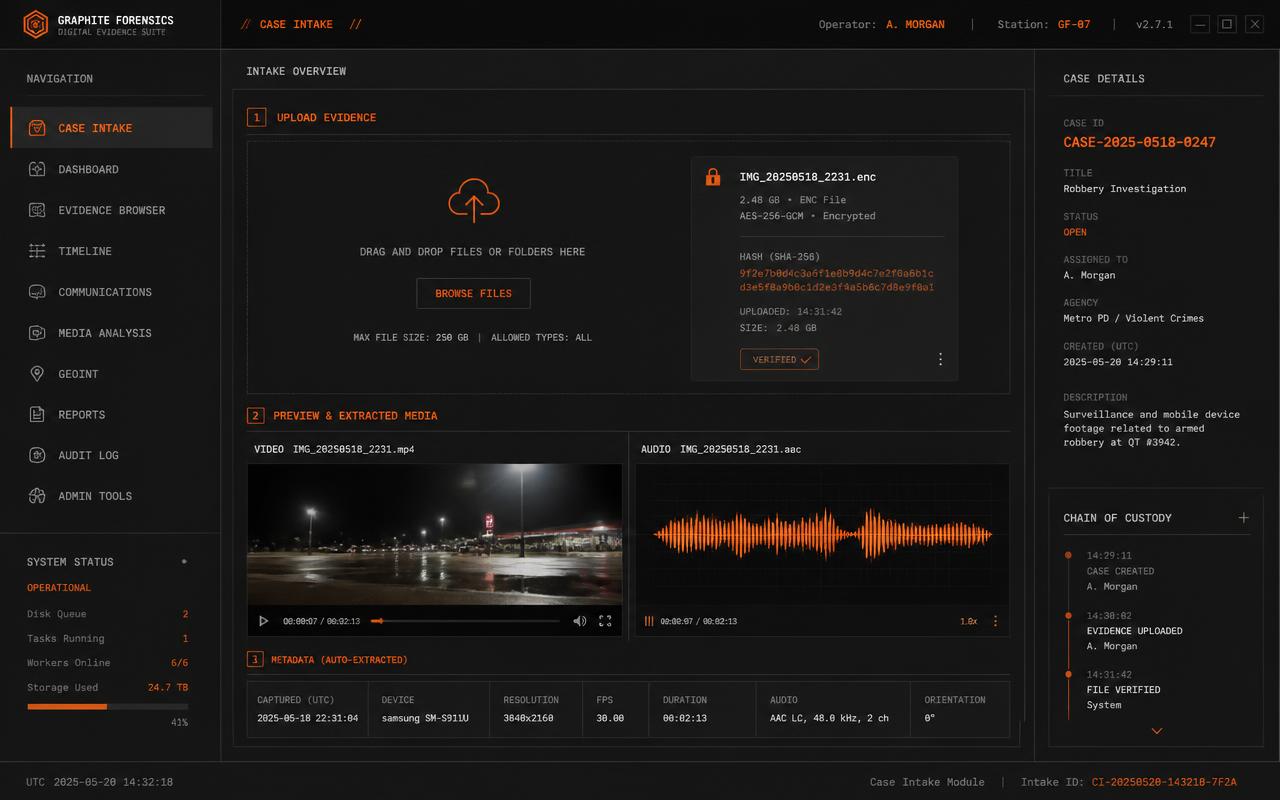
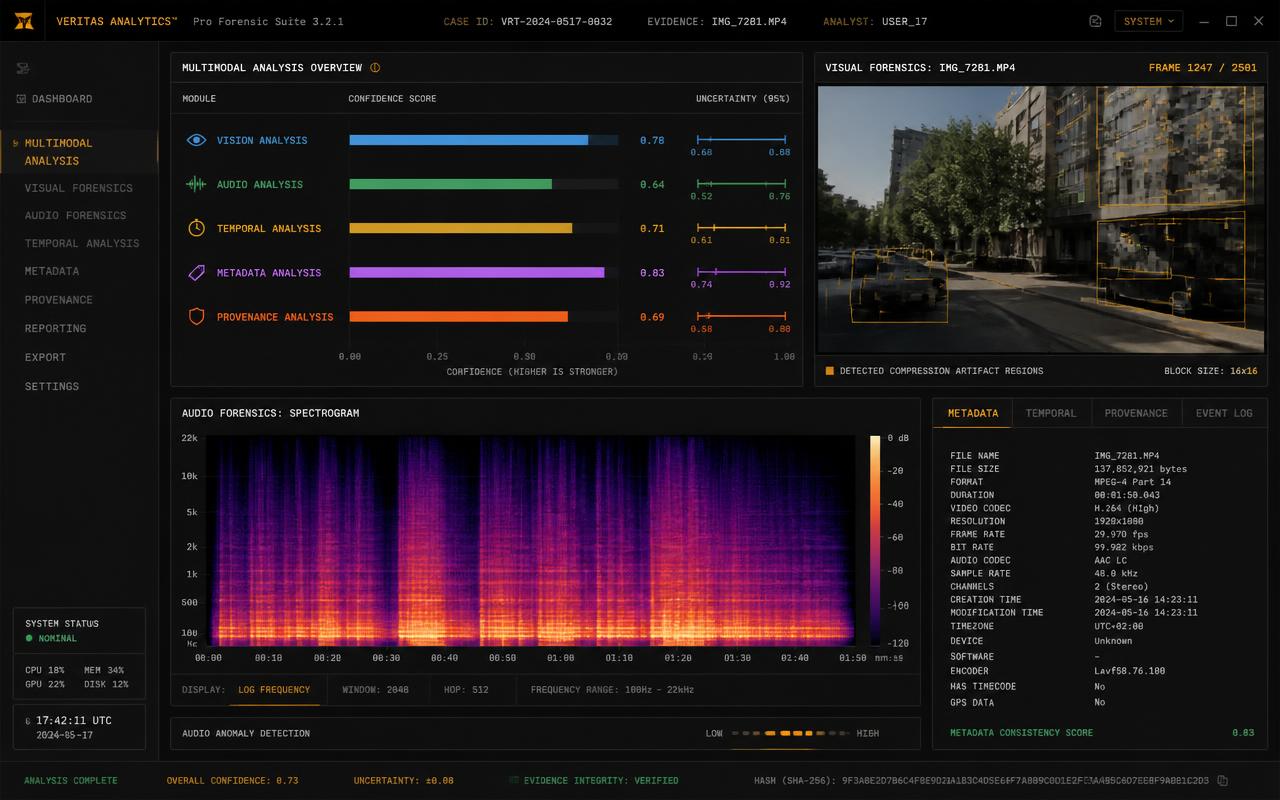
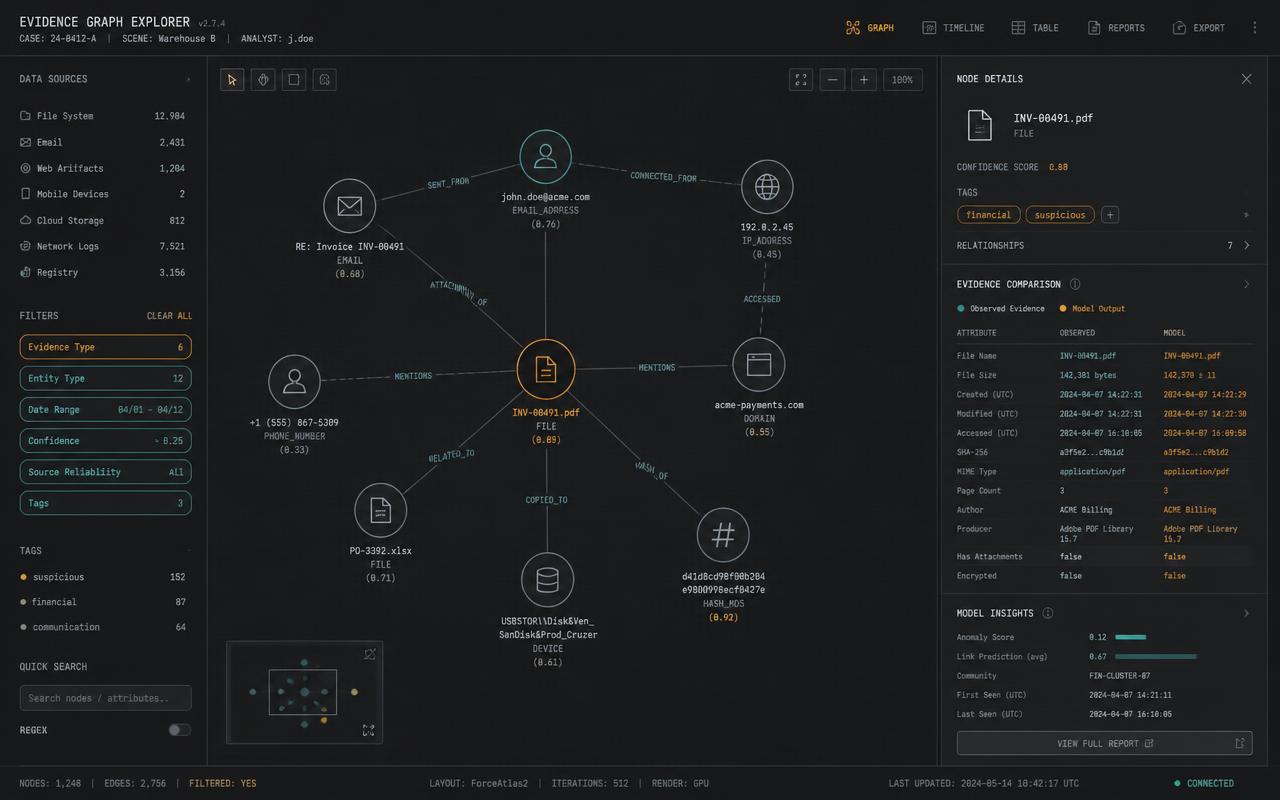
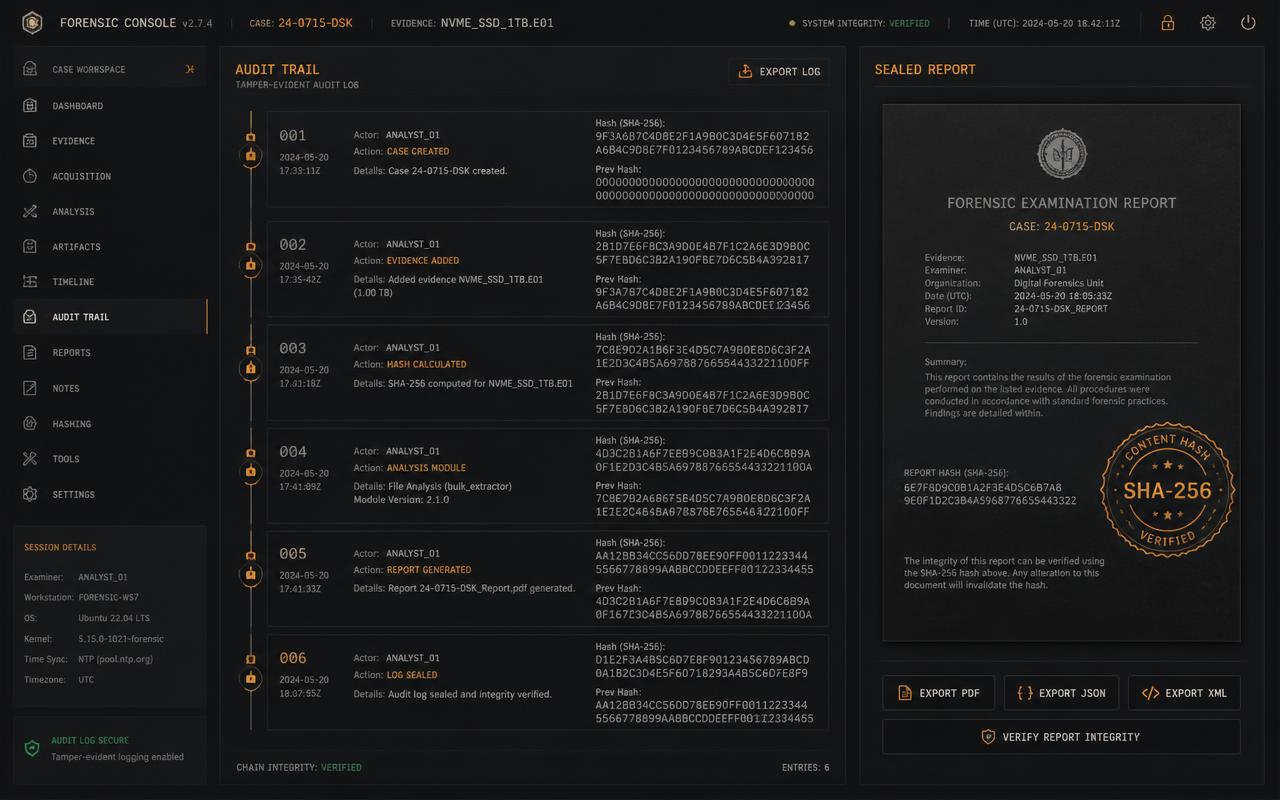
Illustrative console views · demo corpus only · an AI assessment is not proof of wrongdoing
Public walkthrough · demonstration corpus
One case, end to end
Case A — Synthetic video indicators — follow the same case a signed-in analyst would work: ingest and custody, multimodal analysis, reviewer sign-off, then the sealed report digest. Read-only, nothing here is a verdict about a person.
Submitted media
Custody opened
sha256 8428f5d504a875558428f5d504a875558428f5d504a875558428f5d504a87555
- CASE_CREATEDorchestrator
Investigation record created
- MEDIA_UPLOADEDorchestrator
Media ingested and hashed
- ANALYSIS_STARTEDorchestrator
Analysis run dispatched to orchestrator
- MODULE_STARTEDorchestrator
Vision / Audio / Temporal modules started
Demonstration corpus only · an AI assessment is not proof of wrongdoing
Capabilities
What the platform does
Multimodal evidence fusion
Visual, audio, temporal, metadata and provenance modules produce independent evidence, fused with explicit uncertainty.
Encrypted at rest, per user
Uploaded media is sealed with AES-256-GCM envelope keys; decryption stays server-side and role-gated.
Tamper-evident custody
Every action is hash-chained and anchorable, with sealed receipts for each export and report.
Human-in-the-loop review
Mitigation and report finalisation stay blocked until an authorised reviewer signs off with reason codes.
Metered AI gateway
Injection-hardened gateway with Zod-validated inputs, tier limits and per-call audit anchoring.
Agent (MCP) integrations
OAuth-scoped read-only tools for investigations, evidence graphs and sealed provenance bundles.
Workflow
From ingest to sealed report
Scroll through the custody pipeline. Every stage writes a hash-chained audit entry, so the path from raw bytes to conclusion stays reconstructable.
stage 1 / 4
- 01
Sign in
Zero-trust accounts with unique analyst handles and per-user encryption keys.
- 02
Ingest
Upload media into a case; bytes are encrypted before they ever reach storage.
- 03
Analyse
Forensic modules emit evidence with confidence and uncertainty, never verdicts.
- 04
Review & seal
A reviewer signs off; reports export with SHA-256 seals and audit receipts.
An AI assessment is not proof of wrongdoing
Every output is probabilistic and provisional until an authorised analyst reviews it. Suryakavacham is designed for investigative support and research — it does not issue verdicts about people, and its assessments must not be used as sole grounds for action.